



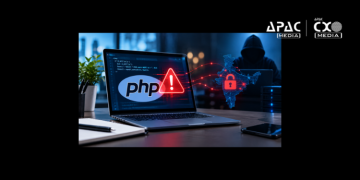


New Delhi, Oct 23(APAC Media): Two critical PHP security flaws have triggered urgent warnings for website operators in India, with CERT-In advising users to address the risks.
The vulnerabilities, identified as CVE-2026-109618 and CVE-2026-109619, could allow attackers to execute malicious code on affected servers under certain conditions. The flaws were disclosed on October 20, prompting cybersecurity agencies to urge organisations to secure vulnerable systems.
PHP Security Vulnerabilities: Why India Is At Risk
India’s cybersecurity agency, the Indian Computer Emergency Response Team (CERT-In), issued a critical-severity advisory on October 21. The warning is relevant to businesses, government departments, hosting providers and website operators that rely on PHP-based applications.
PHP powers widely used platforms such as WordPress and Laravel. Since the vulnerabilities affect the PHP engine, updating a website’s content management system alone may not resolve the underlying security risk.
A successful remote code execution (RCE) attack could allow hackers to run malicious code on an affected server, potentially leading to data theft, website tampering or further system compromise.
PHP Releases Security Patches
The PHP team released security updates for affected branches, including PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Administrators should check their installed versions and apply the appropriate fixes.
The vulnerabilities received a severity score of 9.2 out of 10 under CVSS 4.0. Their potential impact depends on the software version, server configuration and deployment environment.
What Indian Organisations Should Do
Organisations should identify internet-facing systems running PHP, verify their versions and install the relevant security updates immediately. They should also check hosting-provider advisories, review server configurations and investigate suspicious activity.
Systems that cannot be patched promptly may need access restrictions or temporary isolation, based on their exposure and risk. Organisations should also review third-party software and unsupported PHP installations.
The incident highlights the need to secure the software underlying websites, particularly where systems process sensitive customer or government data. Prompt patching and verification remain essential to reducing the risk of exploitation.